Security & Fintech · 2026
Chakra
Android banking fraud intelligence: finds fake banking apps, takes them apart in a Frida…
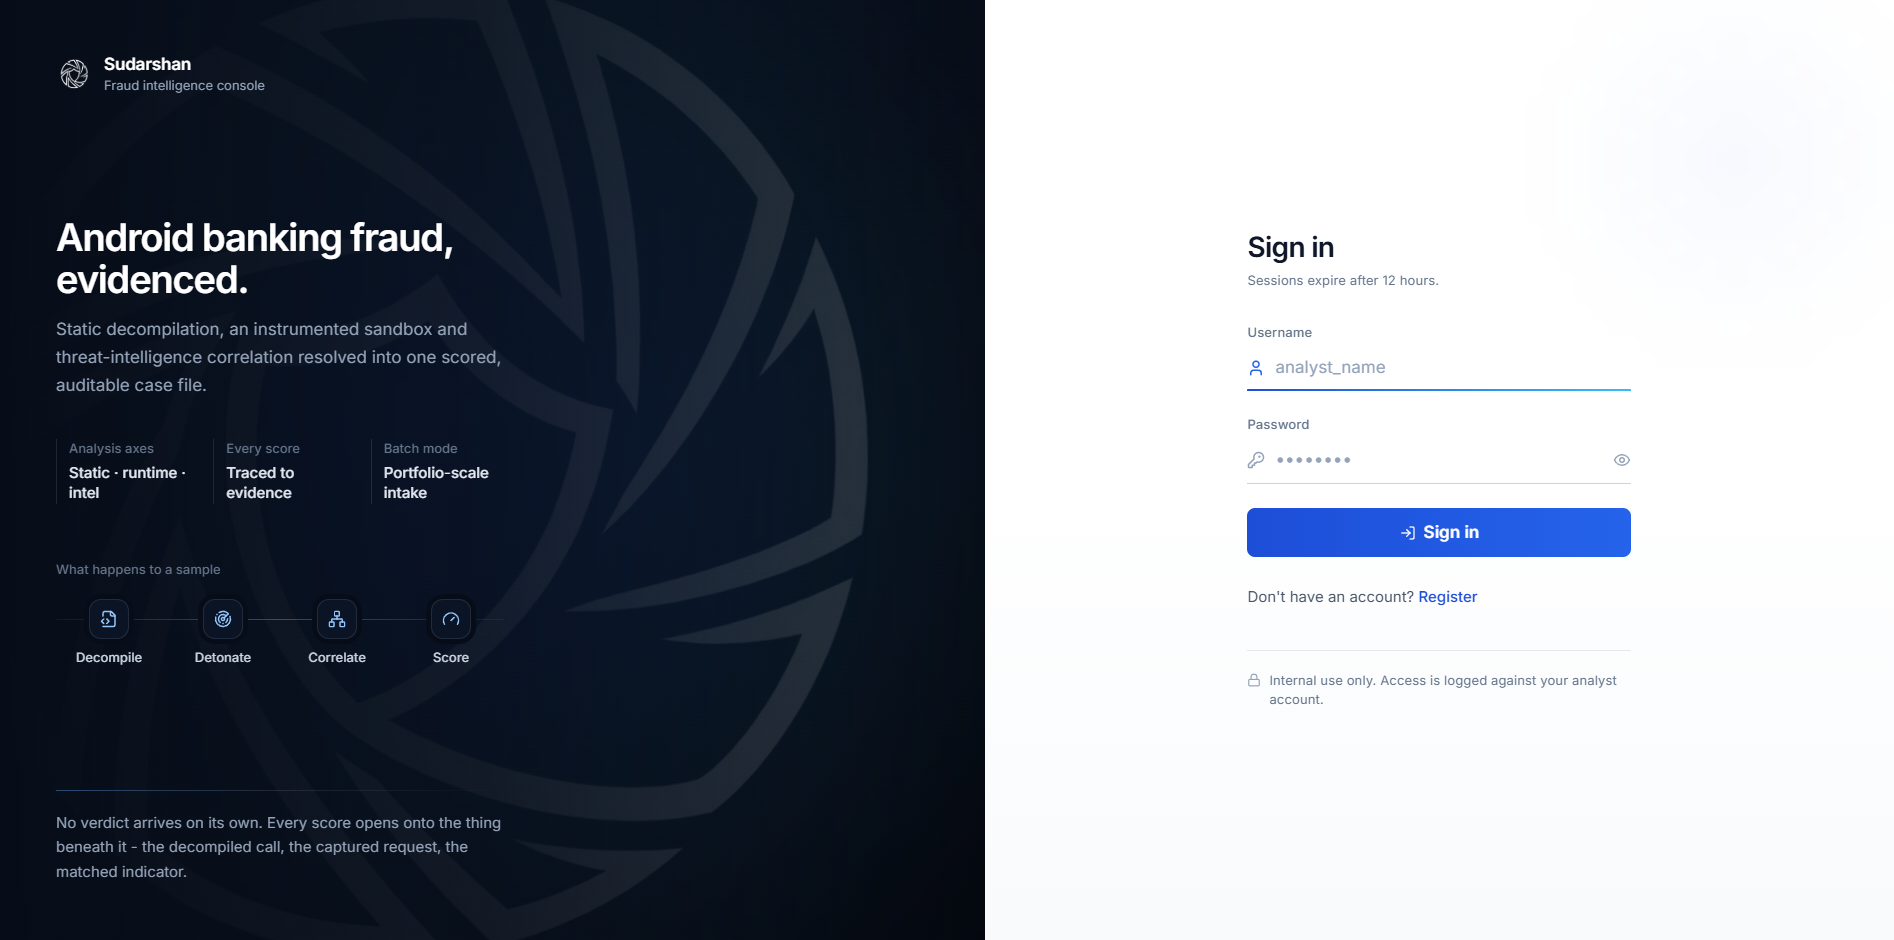
Android banking fraud intelligence: finds fake banking apps, takes them apart in a Frida sandbox and tells the bank exactly what to do next.
Your bank's app has a twin. It looks the same, it asks for the same PIN, and it empties the account in 90 seconds. Chakra finds the twin, takes it apart, and tells the bank exactly what to do next.
The app you install looks right. It has the same blue, the same logo and the same fonts. It politely asks you to "enable Accessibility protection to keep your account safe." You tap Allow.
What it does
- Decompile. It rips the APK open with Androguard, JADX and APKTool. It even repairs APKs that were deliberately corrupted to crash analysis tools. Then it asks whether the app is pretending to be a bank.
- Detonate. It launches the app inside a sealed Android sandbox, with Frida hooks on every sensitive API. An autonomous agent taps through login screens and dialogs to coax out hidden behaviour.
- Correlate. It checks hashes and every contacted domain against VirusTotal, AlienVault OTX and AbuseIPDB, and matches behaviour to known trojan families.
- Score. A deterministic engine turns all of that evidence into one Fraud Risk Score. Same APK, same score, every time, and every point traces back to a piece of evidence.
Built with
- Python
- Android security
- Banking fraud
- Cybersecurity
- Frida
- Malware analysis
- React
- Threat intelligence