Security & Fintech · 2026
Sudarshan
Android banking malware sandbox and threat intelligence platform
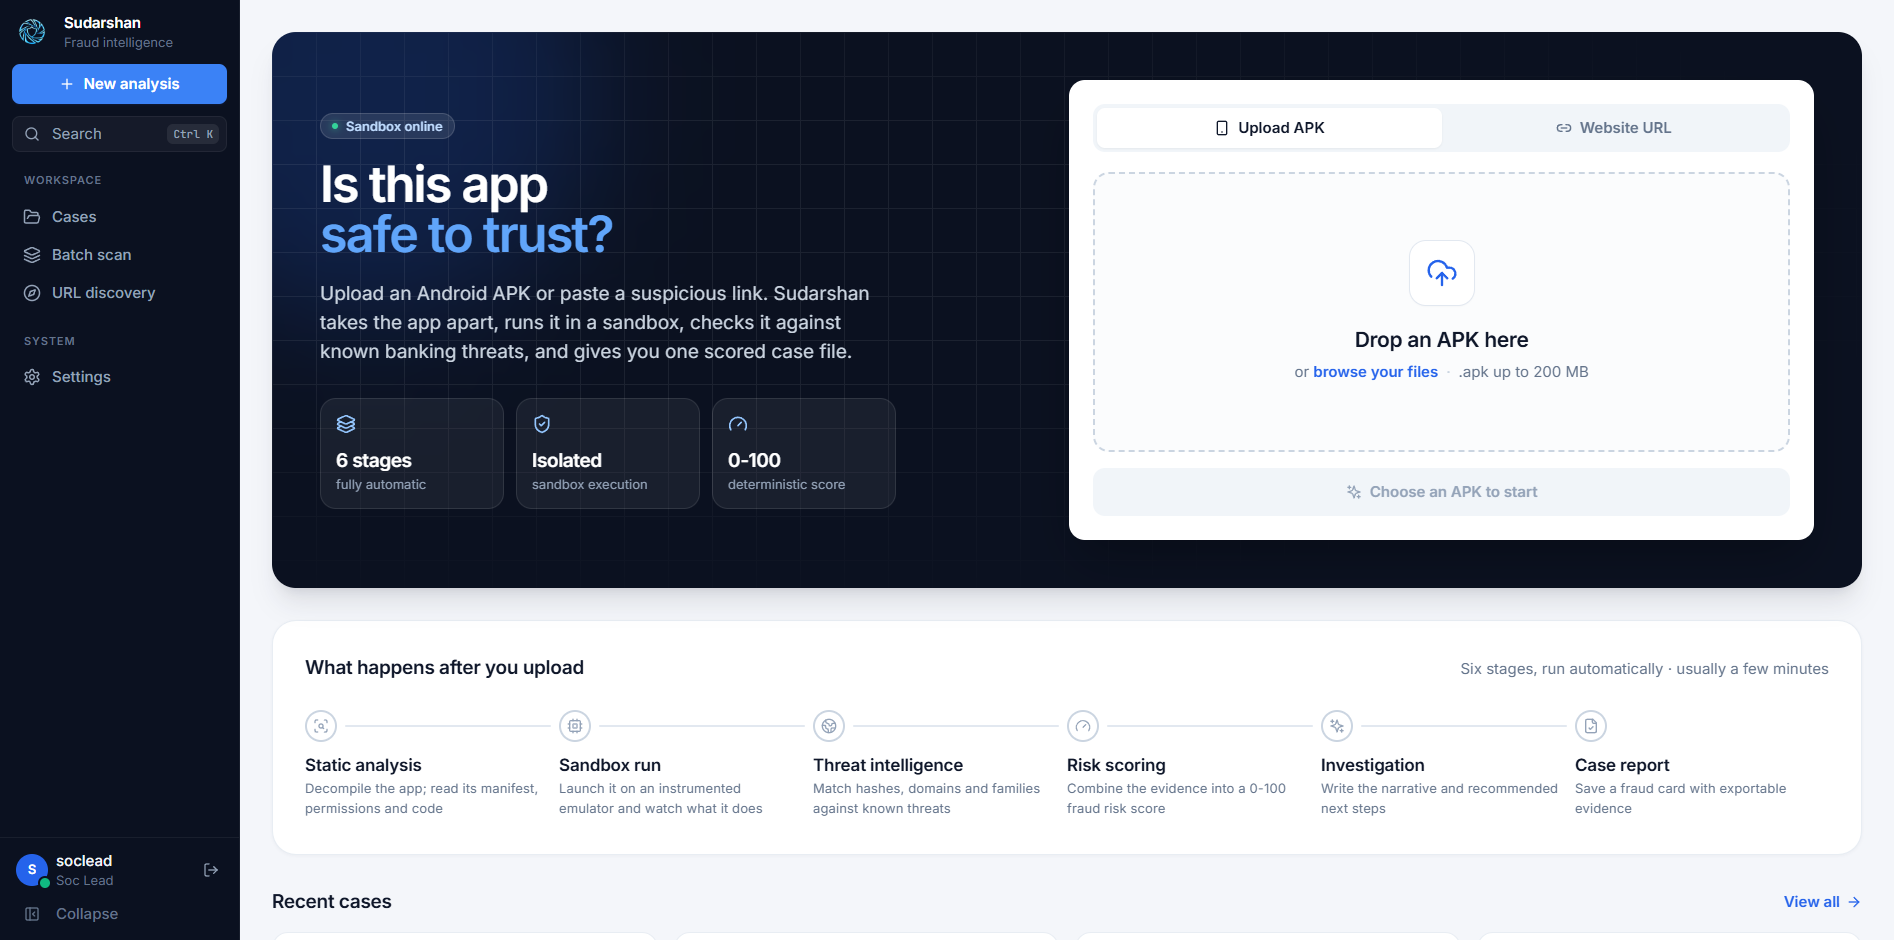
Sudarshan analyses suspicious Android banking apps in a Frida sandbox, captures the command-and-control servers they talk to, and gives each one a deterministic 0–100 risk score.
Fake banking apps copy the real app's look, ask for the same PIN and drain the account within minutes. Families like Drinik, Xenomorph, SOVA, Anubis, Cerberus, Hydra, Octo and Teabot abuse a single Accessibility permission to read the screen, draw a fake login over the real app and swallow OTP messages. A fresh build usually gets 0 detections on VirusTotal, so a bank's fraud analyst learns nothing useful from antivirus alone.
Sudarshan takes a suspicious APK, decompiles and repairs it, runs it in a Frida-instrumented Android sandbox, captures the C2 servers it contacts, checks every indicator against threat intelligence feeds and produces a reproducible risk score. A Gemini assistant then answers analyst questions using only the evidence collected for that case.
What it does
- Decompiles APKs with Androguard, APKTool and JADX, and repairs the malformed ZIP and AndroidManifest headers malware authors use to crash analysis tools
- Live Frida hooks on Accessibility Services, overlay APIs (SYSTEM_ALERT_WINDOW) and SMS receivers, with a UI agent that clicks through prompts and anti-emulation tricks
- A mitmproxy sidecar captures C2 domains, IPs and beacons, cross-checked against AlienVault OTX, AbuseIPDB and VirusTotal and mapped to MITRE ATT&CK
- Deterministic Banking Fraud & Cyber Threat Index (BFCI): every score is auditable and reproducible
- Built on one rule: “The Engine Decides, The AI Explains.” The assistant cites case evidence and cannot change the score
Built with
- Python
- Frida
- Androguard
- JADX
- APKTool
- mitmproxy
- Gemini
- Docker
- MITRE ATT&CK